Search

Build with Claude.
Secure with Palo Alto Networks.
Protect data, govern agents and control AI costs.

Challenges
Why Enterprises Need To Secure Claude
Claude Code, Claude.ai and Cowork are now part of everyday work.
Connected files, skills and tools need enterprise visibility and controls.
Connected files, skills and tools need enterprise visibility and controls.

Shadow Claude Adoption
Claude Code or Cowork can be installed on developer endpoints, creating security blind spots.

Compromised Integrations
A compromised server or plugin for agents built on Claude can open an attack path into enterprise workflows.

Sensitive Data Exposure
Proprietary data, customer records and developer credentials can leak through Claude prompts and agent actions.

Uncontrolled Agent Actions
Excessive permissions can cause Claude-powered agents to expose sensitive data or disrupt workflows.
Solution
Securing Claude At Enterprise Scale
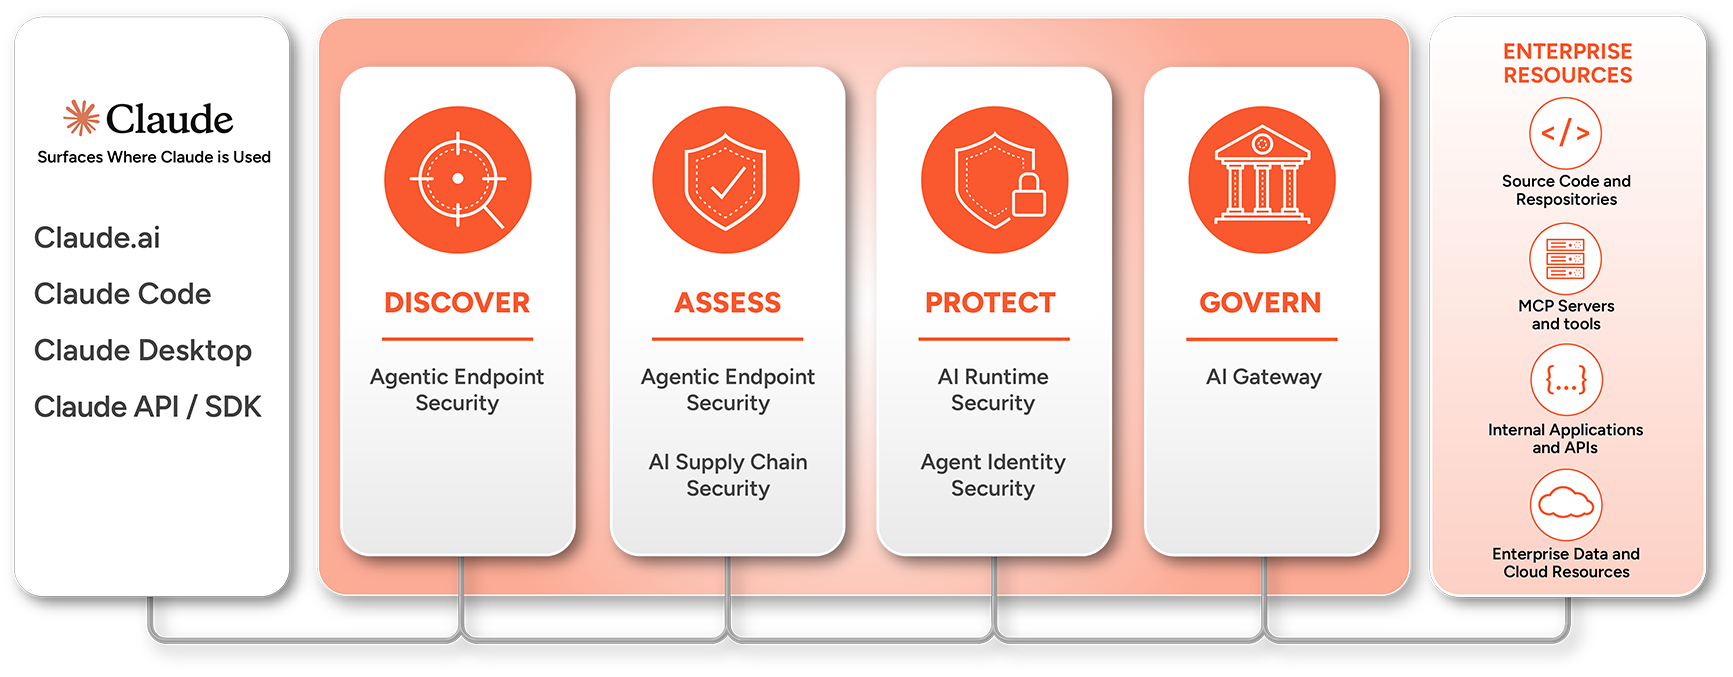
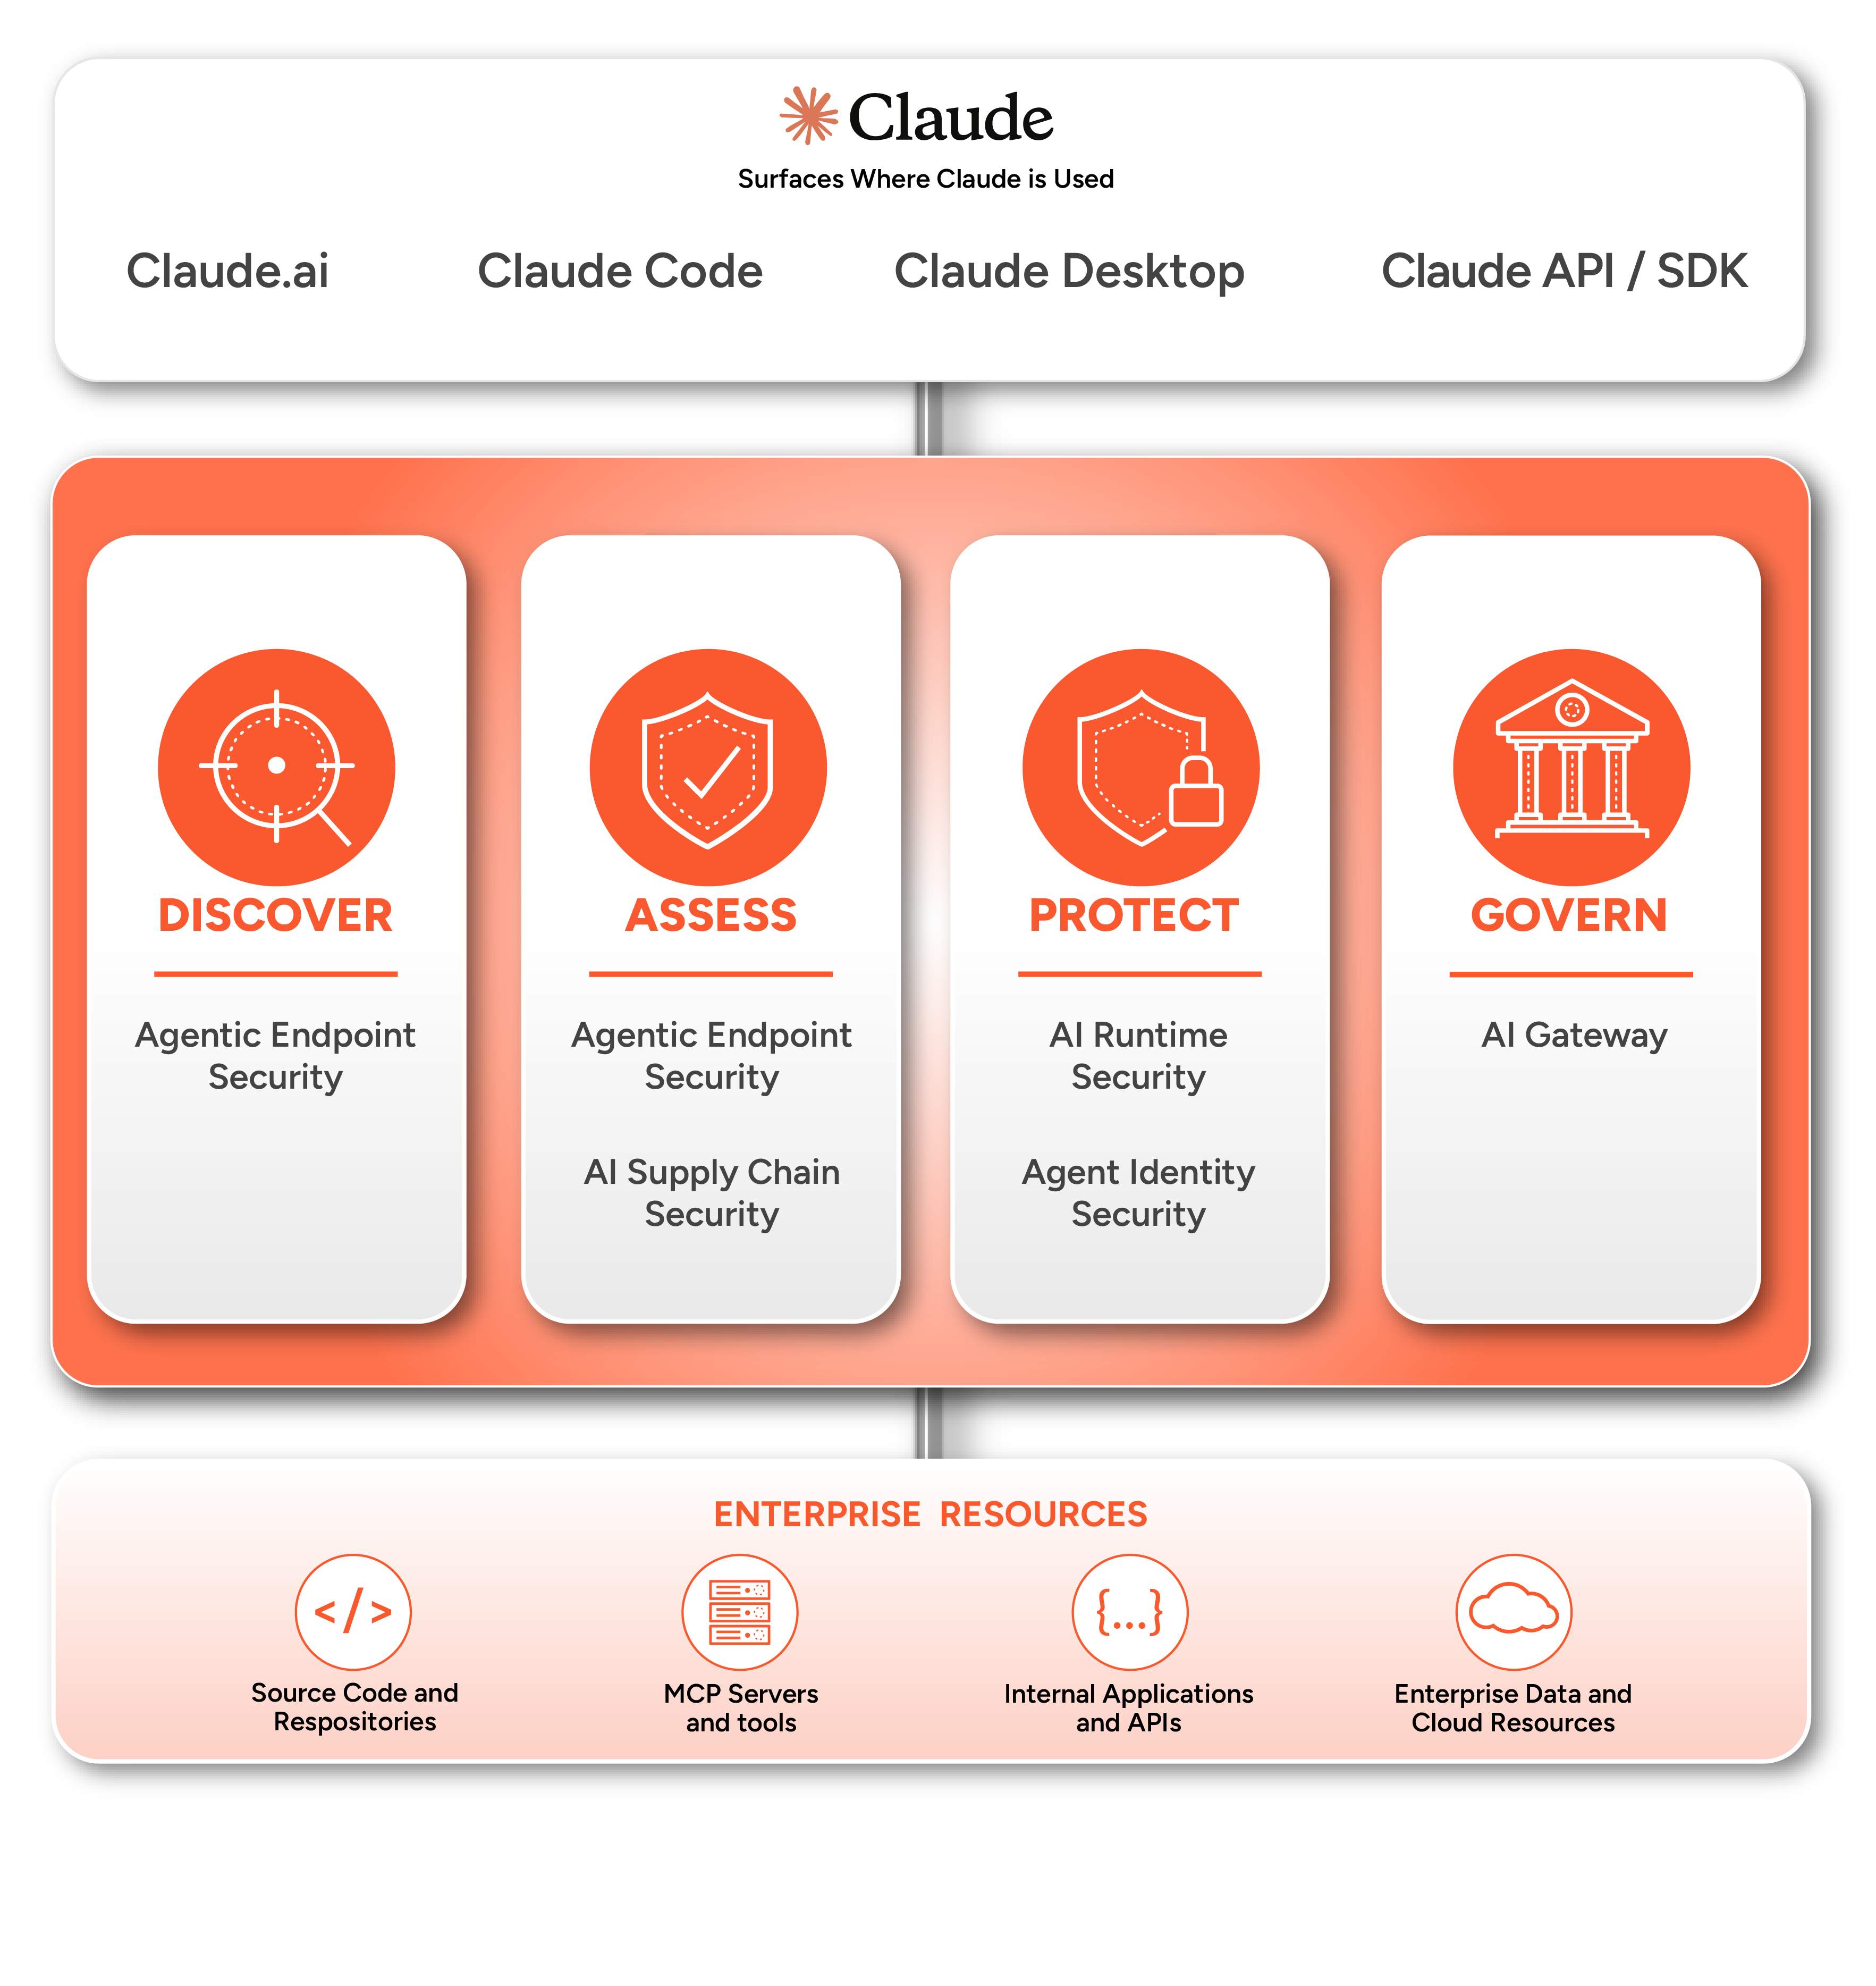
See where Claude runs, secure what it connects to, protect the data it touches and govern the agents it powers.
175T+Claude tokens processed monthly
2.4B+Claude requests processed monthly1
$27MClaude spend governed daily
75,000customers protected worldwide
1,000+ pre-defined DLP patterns
99.24% direct prompt injection prevention rate
75,000customers protected worldwide
1,000+ pre-defined DLP patterns
99.24% direct prompt injection prevention rate
FEATURED WEBINAR
From Claude Code To Cowork: The Security Priorities That Matter
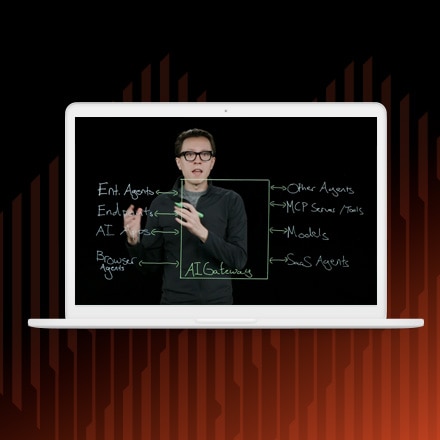
Interested in how Prisma® AIRS™ can help secure your use of Claude? Join us to learn more in this webinar.
Hear how to get started
Understand the risks developers and knowledge workers face, and the identity and security controls that help secure Claude in an enterprise.
Frequently asked questions
Anthropic builds security into the model and platform with controls such as SSO, admin settings and audit logs on enterprise plans. Your organization still decides what Claude can access, which tools connect to it and what data employees share with it. Palo Alto Networks helps you secure and govern Claude across your enterprise.
It complements Anthropic’s safety and security measures by providing enterprise-grade controls. Claude Enterprise controls govern the Claude app. Palo Alto Networks extends visibility and policy to developer endpoints, third-party MCP servers and agent actions across your environments. It also enables you to gain insight into risk on the agent supply chain and agent behavior, and fix any issues.
Claude Code reads files, runs commands, and connects to external tools with the developers’ permissions. Secure it by protecting secrets and source code, vetting extensions, MCP servers and inspecting the context agents read for prompt injection through Cortex AES.
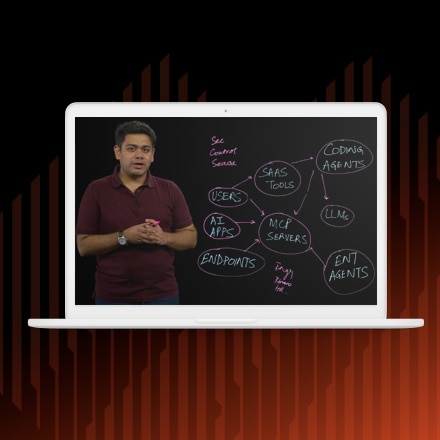
MCP servers let Claude Code, Cowork and custom agents built on the Claude ADK access data and take actions in other systems. A compromised server can trick the agent to leak data or trigger unintended actions. You should inspect MCP servers before use, limit the scope of how MCP servers can be used by an agent and monitor MCP traffic for prompt injections and data leaks.
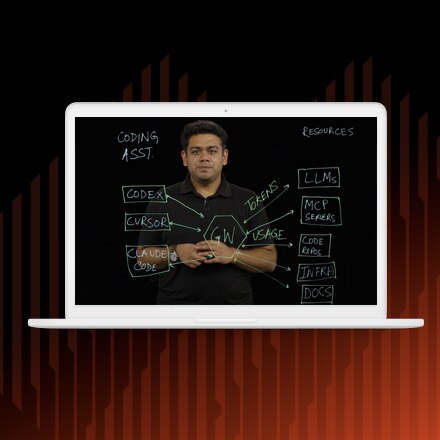
You should treat each agent as an identity with its own scoped, time-bound permissions. Granting just-in-time access to approved systems and revoking access when the task is complete allows risk to be contained. These policies can be centrally enforced on agents through AI Gateway, so that you can also ensure cost-based controls and tool-usage controls.